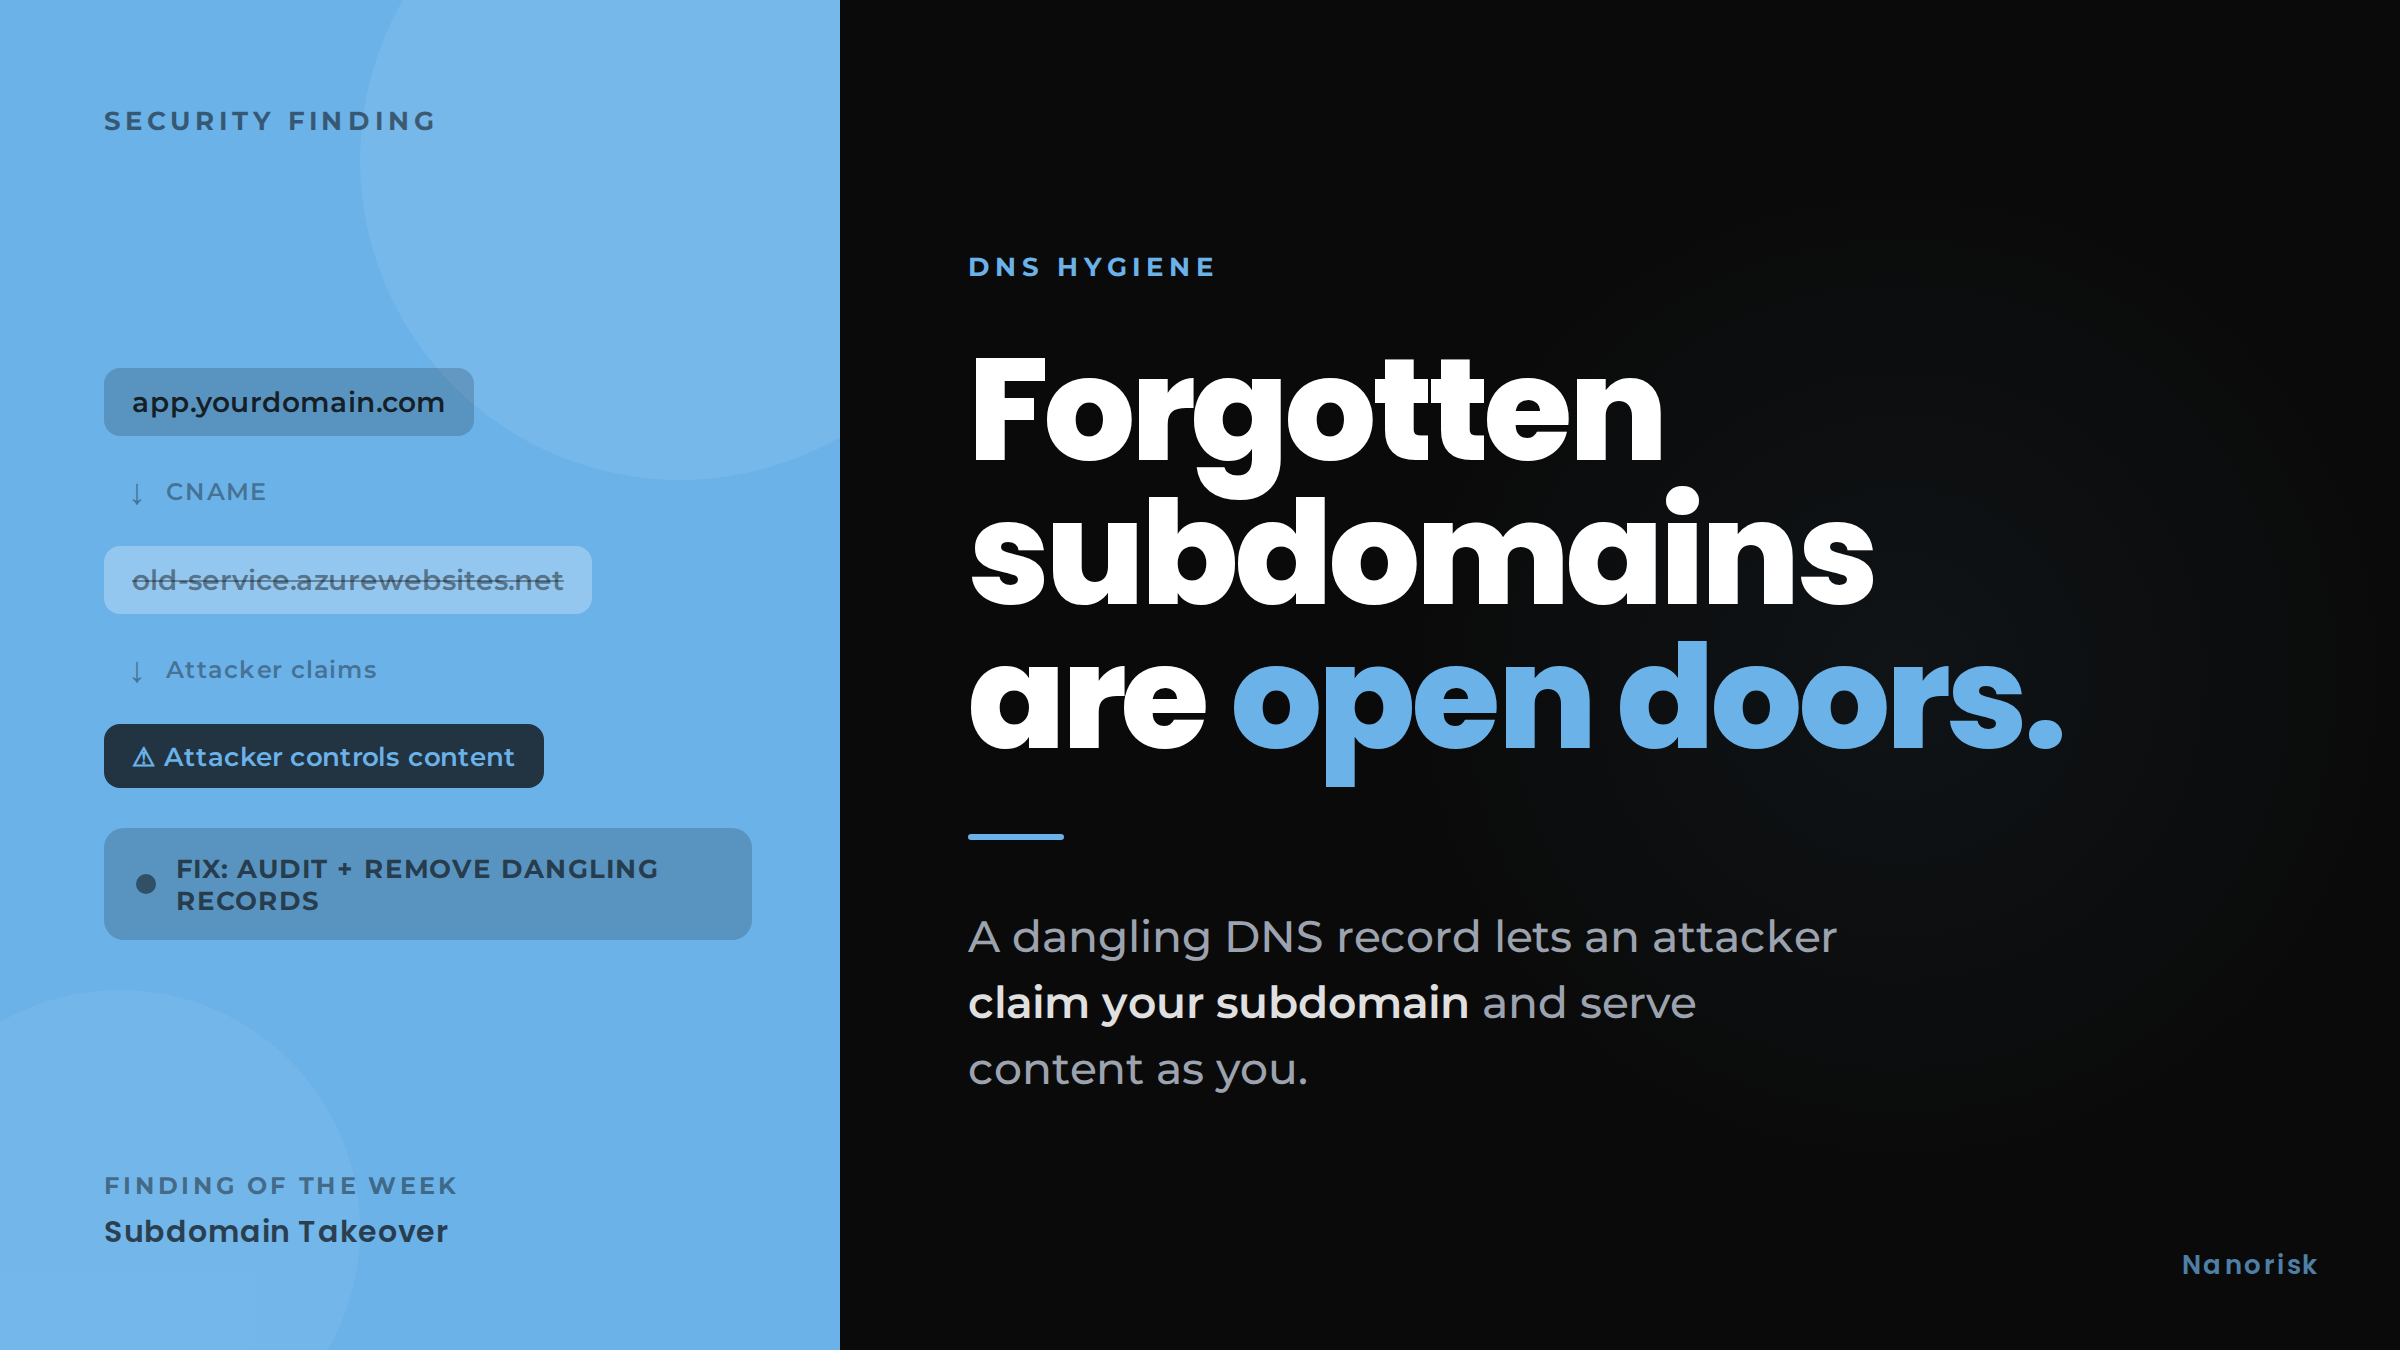
Finding of the Week: subdomain takeover.
This one comes up consistently across external assessments, and the root cause is almost always the same. A cloud service gets decommissioned, the DNS record never gets cleaned up, and months later a CNAME is still pointing at an address that no longer belongs to anyone. In most cloud environments, that means an attacker can simply provision a new resource at that address and claim the subdomain - serving content under your domain, with none of the usual indicators that something is wrong.
The impact is not theoretical. A trusted subdomain carrying an attacker's payload is a meaningful advantage in phishing campaigns, and it undermines any trust signals your users rely on to distinguish legitimate communications from fake ones.
The fix is straightforward in principle: audit your DNS records, remove entries that point at infrastructure that no longer exists, and treat DNS cleanup as a required step whenever a cloud resource is decommissioned rather than something handled separately. The difficulty is usually not technical - it is process. Organisations that do not have a current, maintained inventory of their subdomain footprint cannot easily identify what is dangling. If that describes your situation, an external attack surface review is a practical starting point.