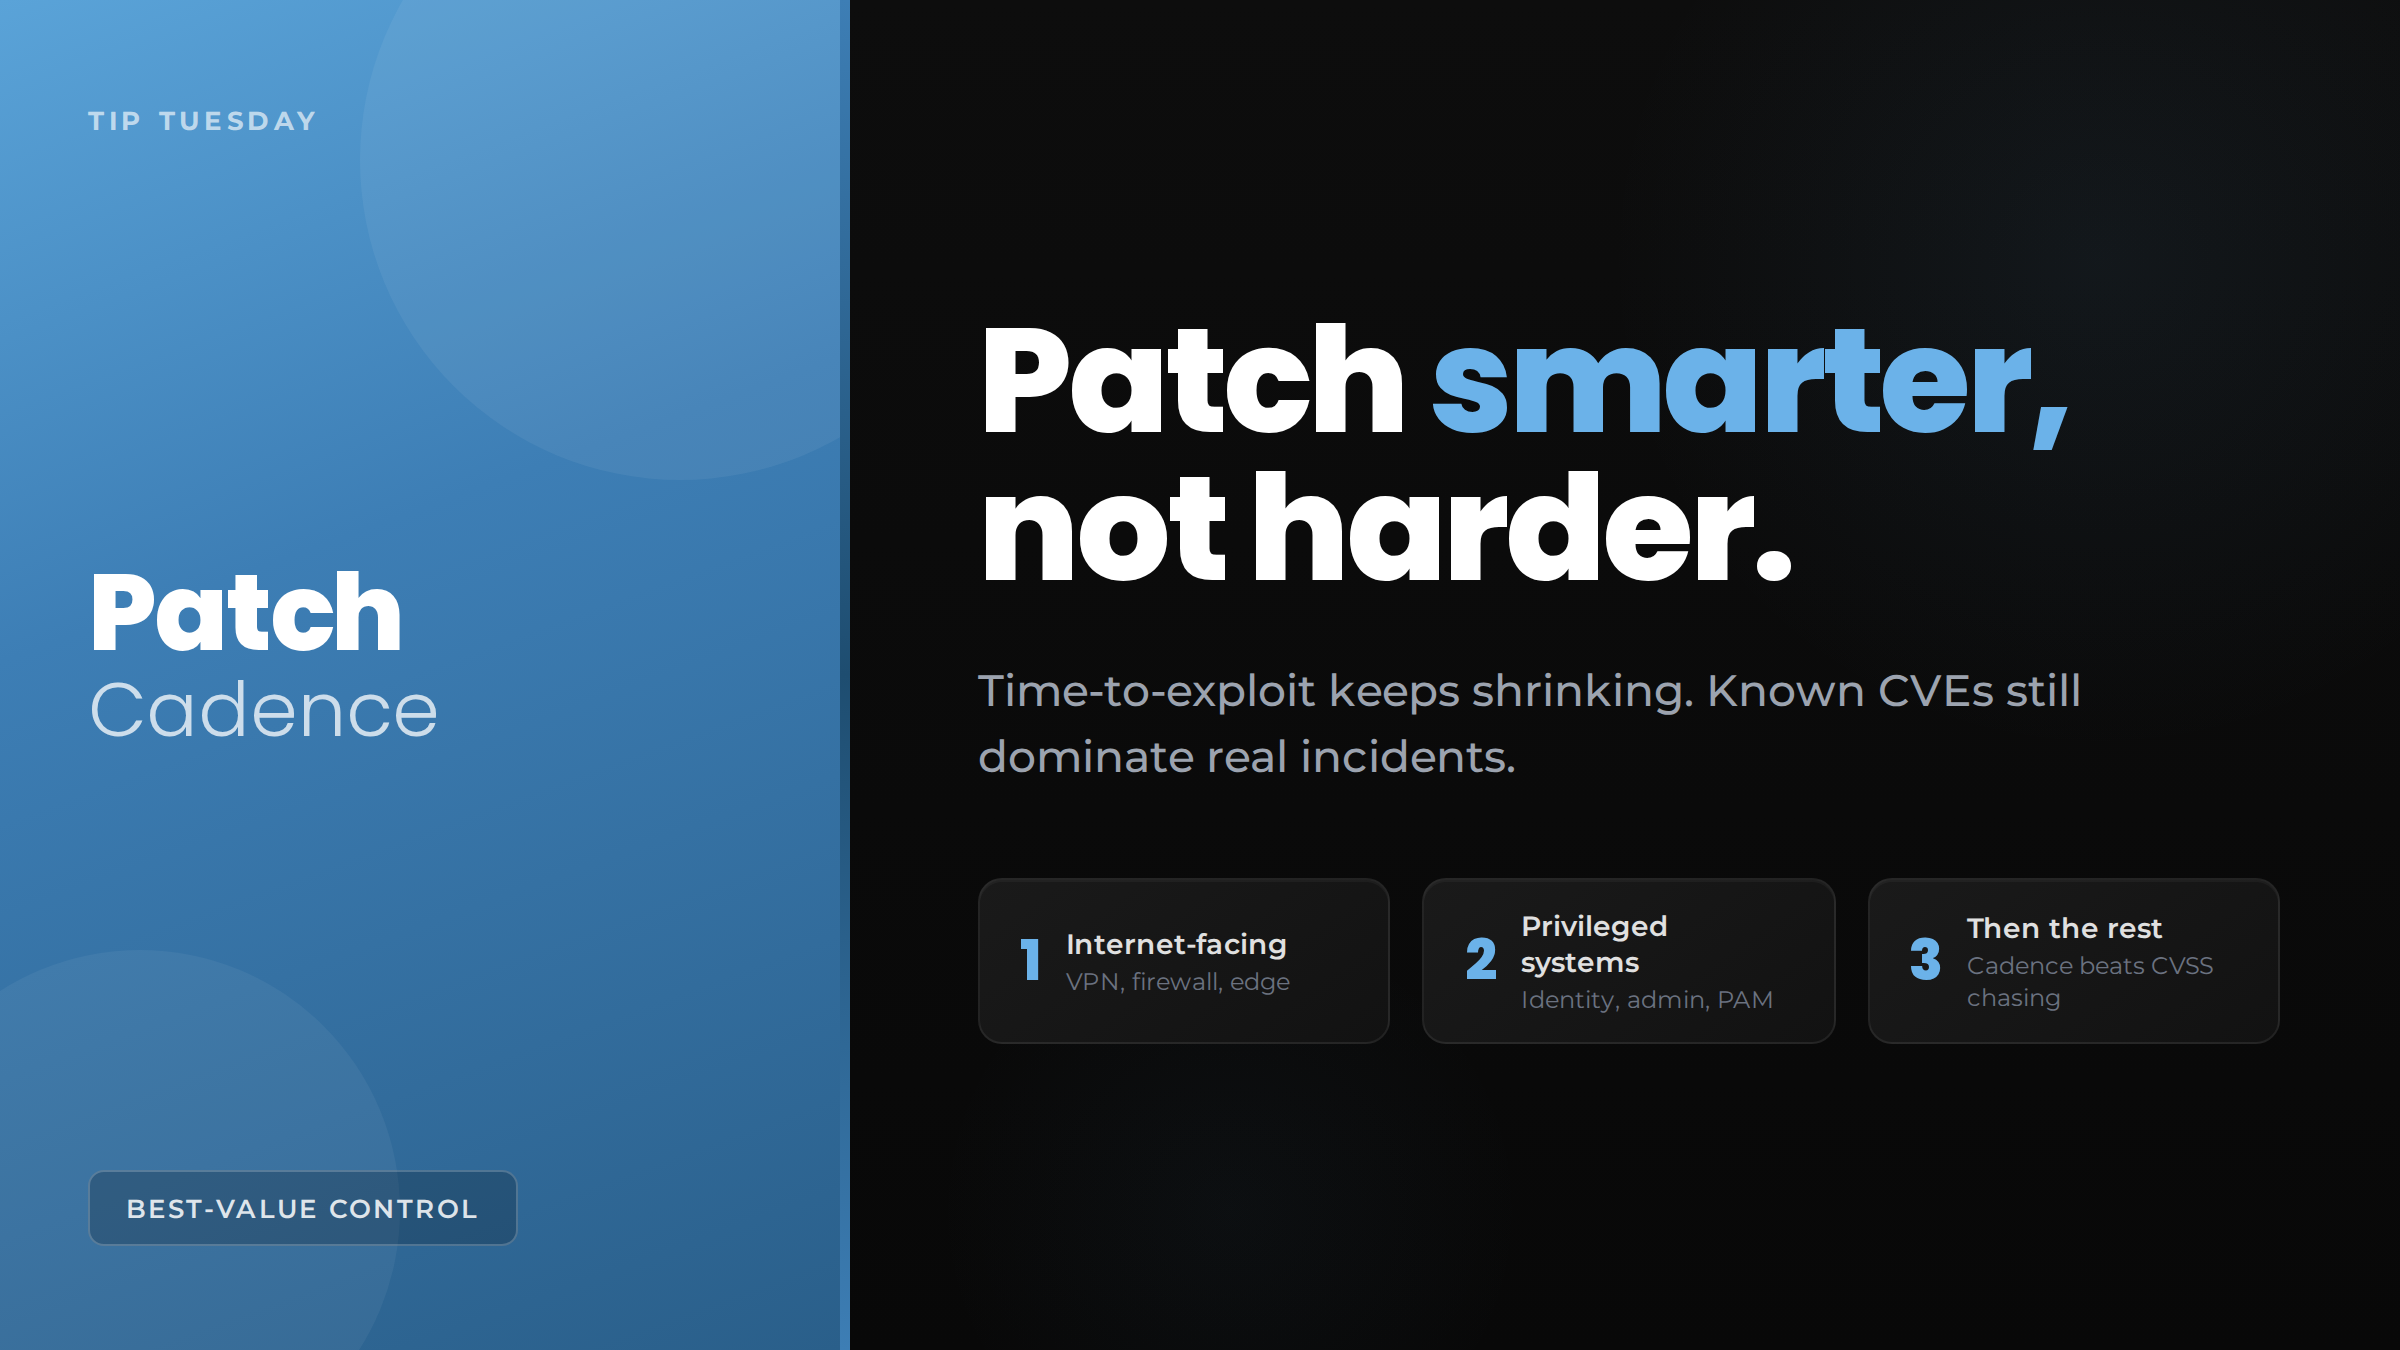
Tip Tuesday: patch cadence is still your best-value control.
Time-to-exploit for known vulnerabilities has shortened considerably over recent years, and the pattern we see across assessments hasn't changed: the majority of real incidents still trace back to CVEs that had patches available. The problem isn't usually a lack of awareness - it's a lack of a consistent, risk-ordered process.
A pragmatic cadence prioritises internet-facing assets and edge devices first - VPN gateways, firewalls, and anything else directly reachable from outside your perimeter. Privileged systems come next. Everything else follows in a structured schedule. Chasing every CVSS 10 regardless of context is rarely the right model; understanding where exposure actually sits is.
If patching gaps are a known problem but the prioritisation isn't clear, an external attack-surface review gives you the asset visibility to make those decisions properly.