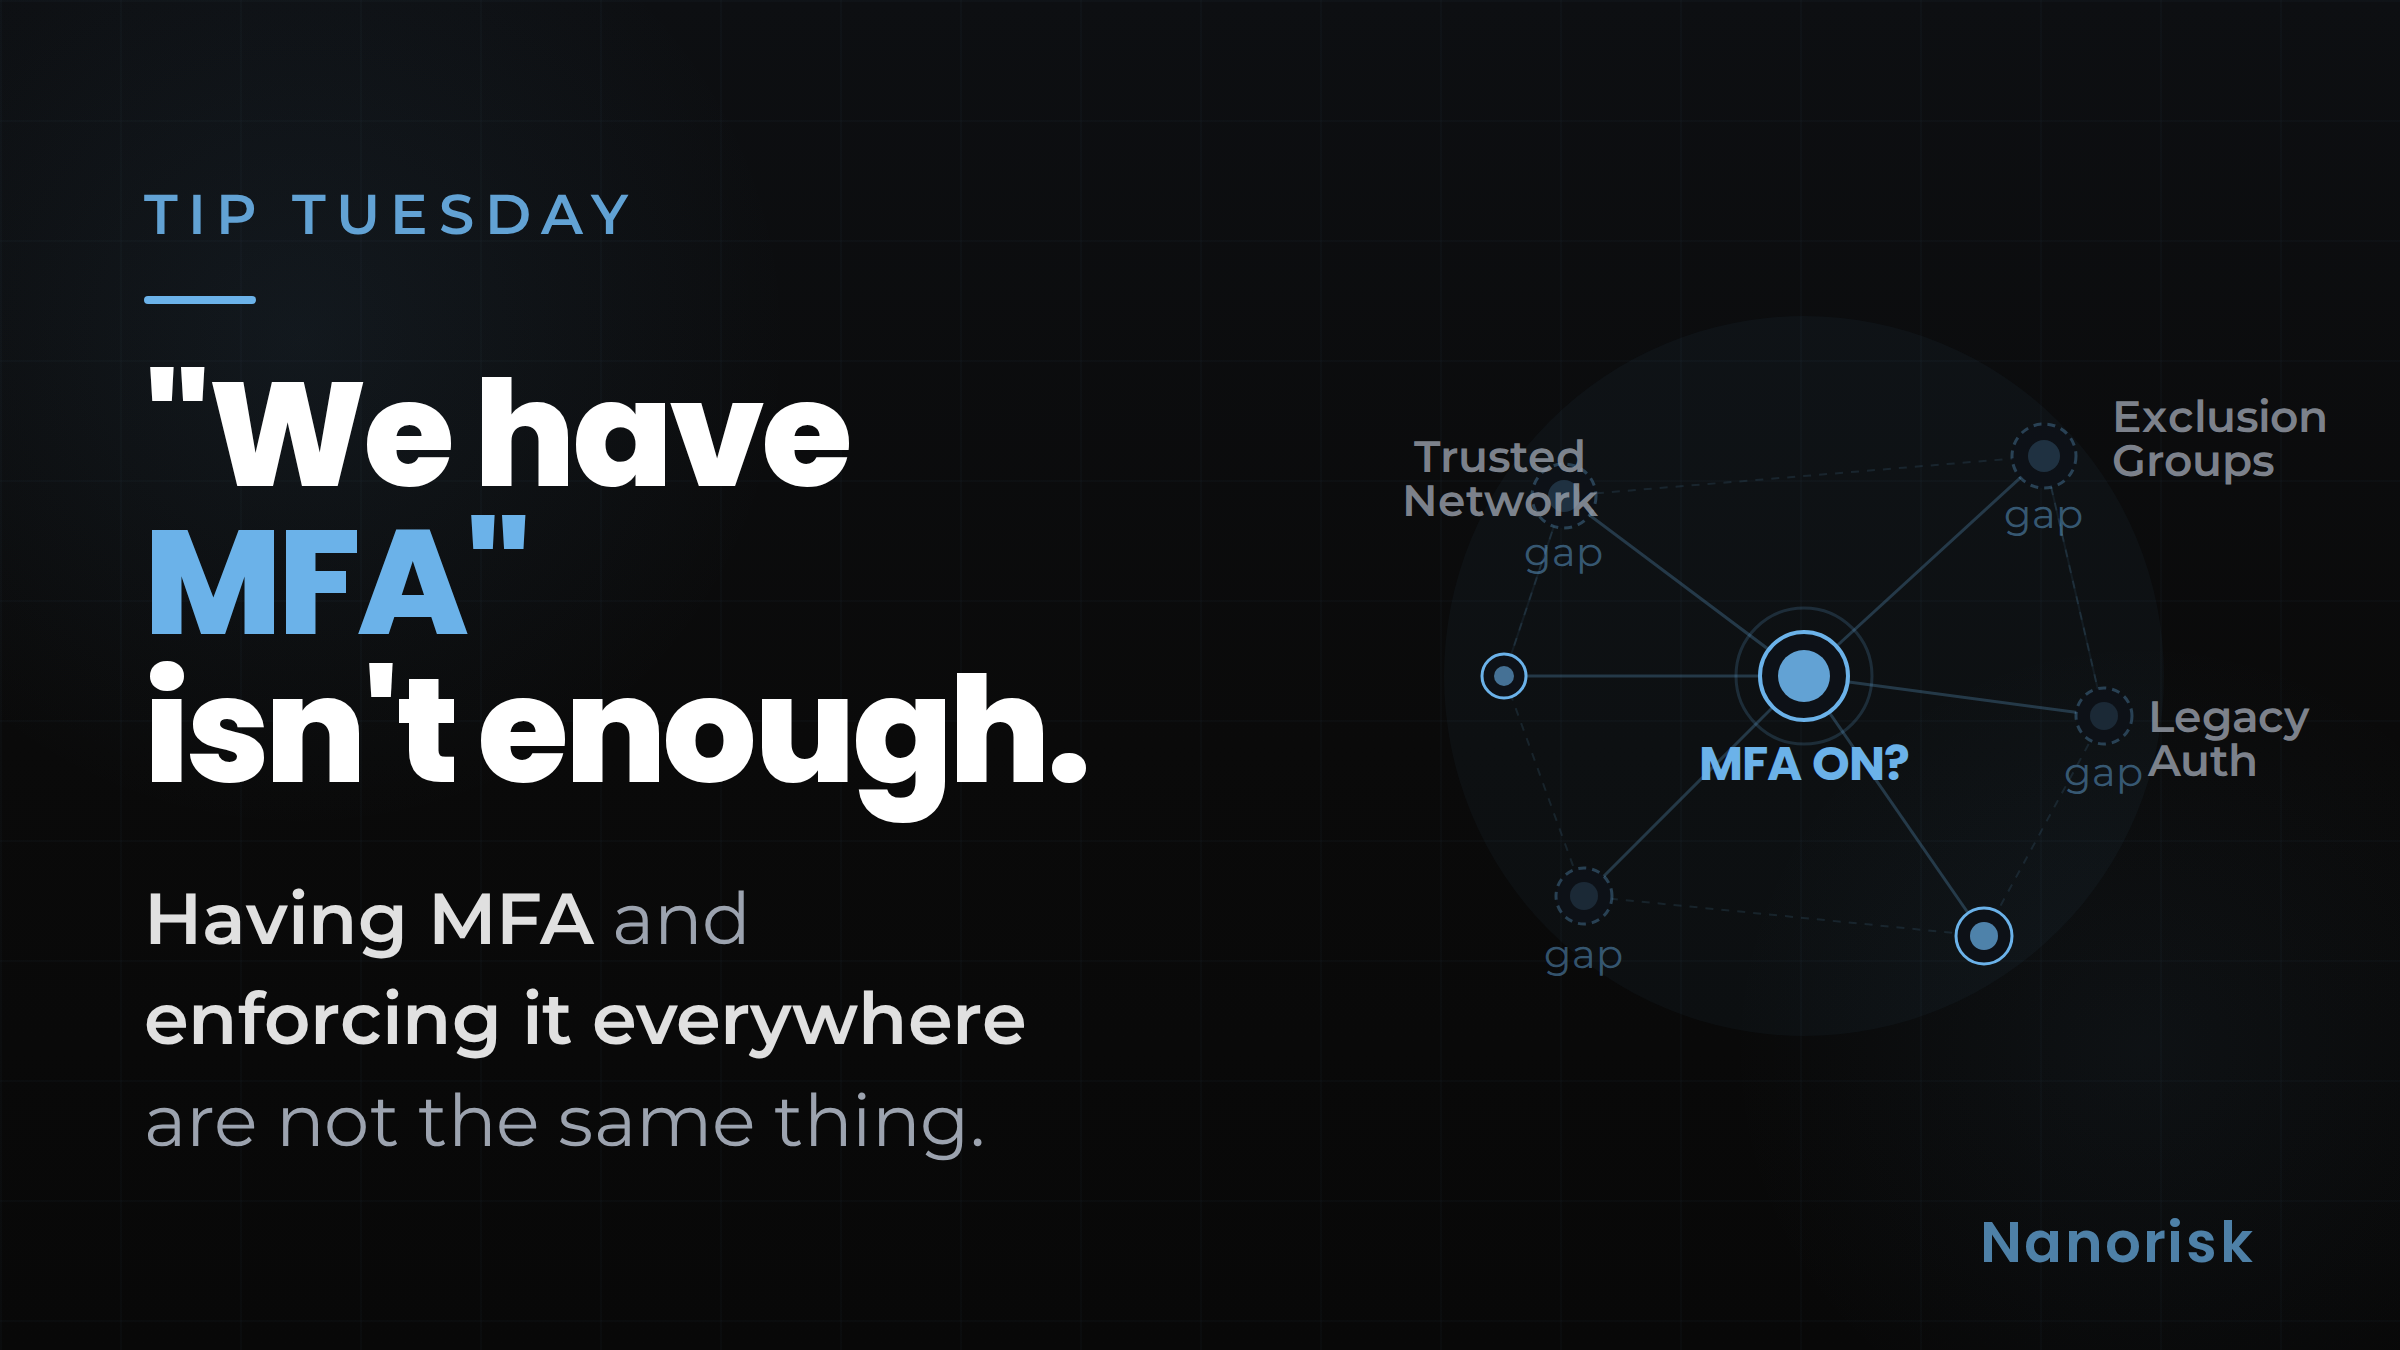
Tip Tuesday: 'We have MFA' and 'MFA is enforced for everyone, everywhere' are different statements, and the gap between them is where accounts get compromised.
Three places where MFA quietly disappears. First, trusted network or location bypasses: conditional access policies that skip MFA when a user authenticates from a known IP range are common and reasonable in isolation, but they create a clear target. If an attacker can route through a trusted egress point or compromise a device already on a trusted network, MFA is out of the picture. Second, exclusion groups: these are added legitimately, usually to unblock a service account or a specific user during troubleshooting, and then they are never reviewed. Over time those groups grow, and so does the excluded attack surface. Third, legacy authentication protocols: SMTP AUTH, IMAP, and basic authentication do not pass through conditional access. Any account that can be reached via those protocols can be attacked with just a password, regardless of what your MFA policy says.
To find out which statement is true in your own tenant this afternoon, open Entra ID, go to Sign-in Logs, and filter for authentications where the MFA requirement was not satisfied or was skipped. Add a filter for legacy authentication client apps while you are there. The results are usually instructive.
If you would like a structured assessment of your Microsoft 365 and Entra ID configuration, we cover exactly this as part of our M365 security review.