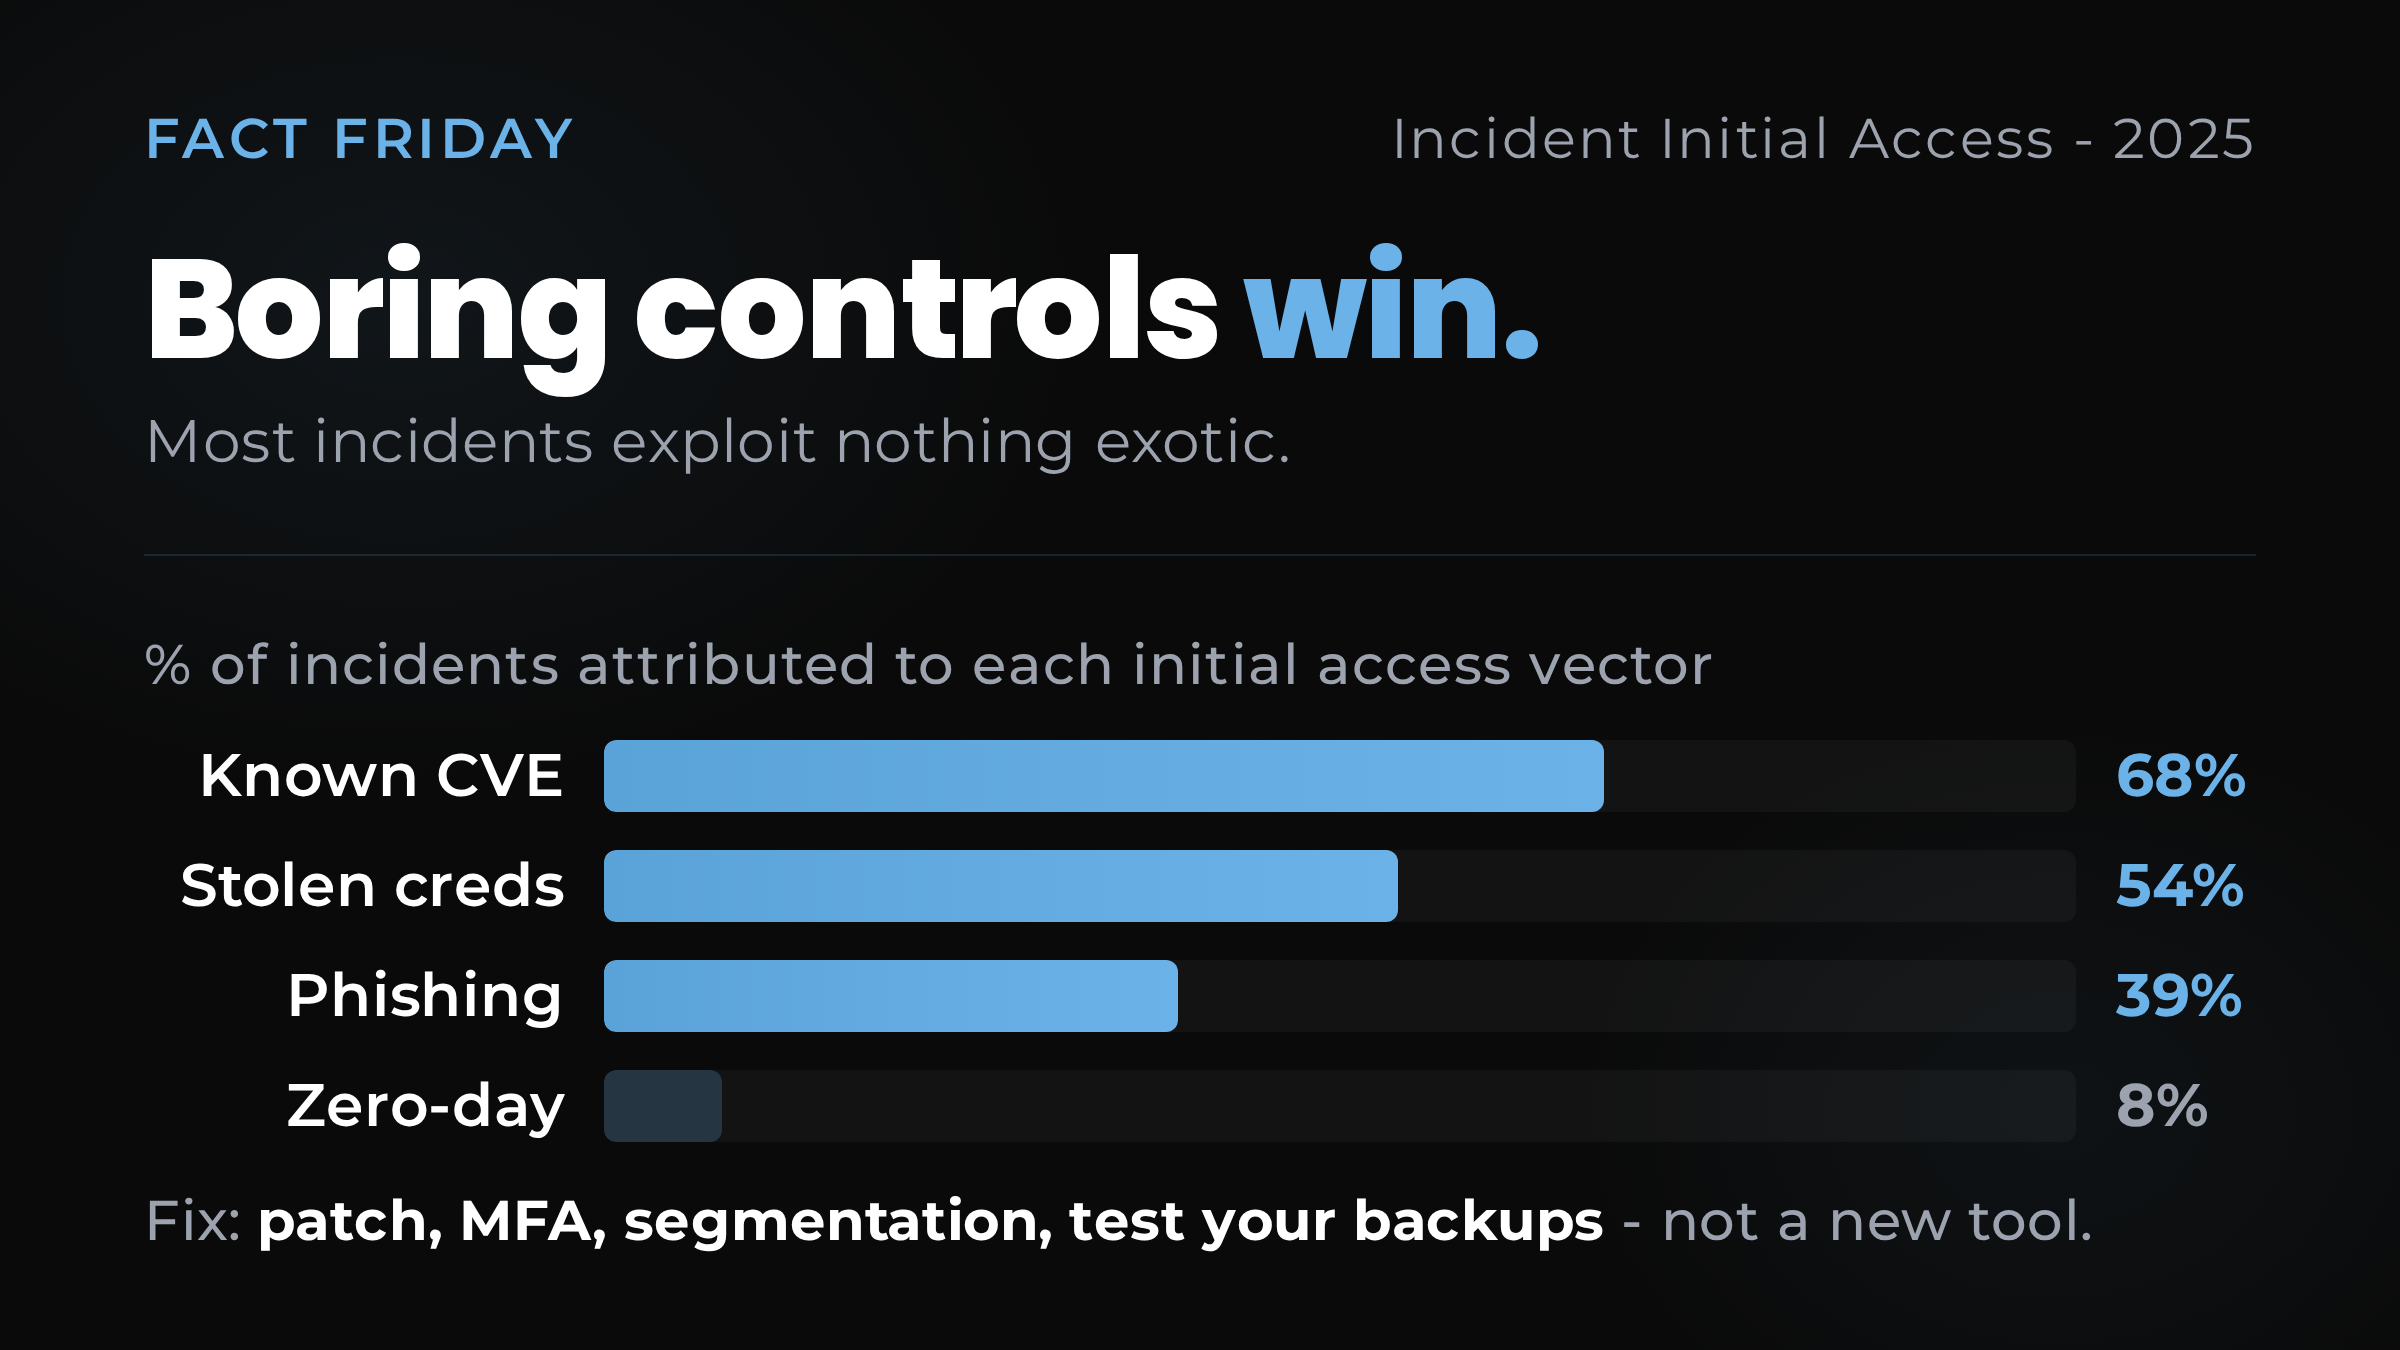
Fact Friday - and the fact is that the controls preventing most incidents are the ones organisations have been told about for years.
Known CVE exploitation is one of the dominant initial access methods across incident reports right now. Identity-based intrusions are rising sharply - credential theft and account takeover working precisely because MFA wasn't enforced or was inconsistently applied. And untested backups remain a widespread problem: the backup job runs, the log shows success, and nobody verifies whether the data actually restores until it matters.
Patching on a structured cycle, enforcing MFA across every account including service accounts and admin access, segmenting networks so a compromised endpoint cannot move freely, and running genuine recovery tests against your backups - these four controls, properly implemented, would close off the majority of the attack paths we see being used in practice.
None of it is sophisticated. That's the point. The unglamorous stuff consistently carries the day.